Penetration testing: Attacks on systems
Connected systems make tempting targets for attackers. Vulnerabilities can go undetected despite even the most diligent development practices. Standardization and regulatory bodies are well aware of the problem and now require penetration tests for certain products (UNECE r155 / ISO 21434, CRA, IEC 62443, FDA guidelines, EU MDR / IEC 81001-5-1, DO-326A / ED-202A, DO-356A / ED-203A, NIS 2). To this end, penetration testers take on the mantle of attackers in an attempt to identify vulnerabilities in the system.
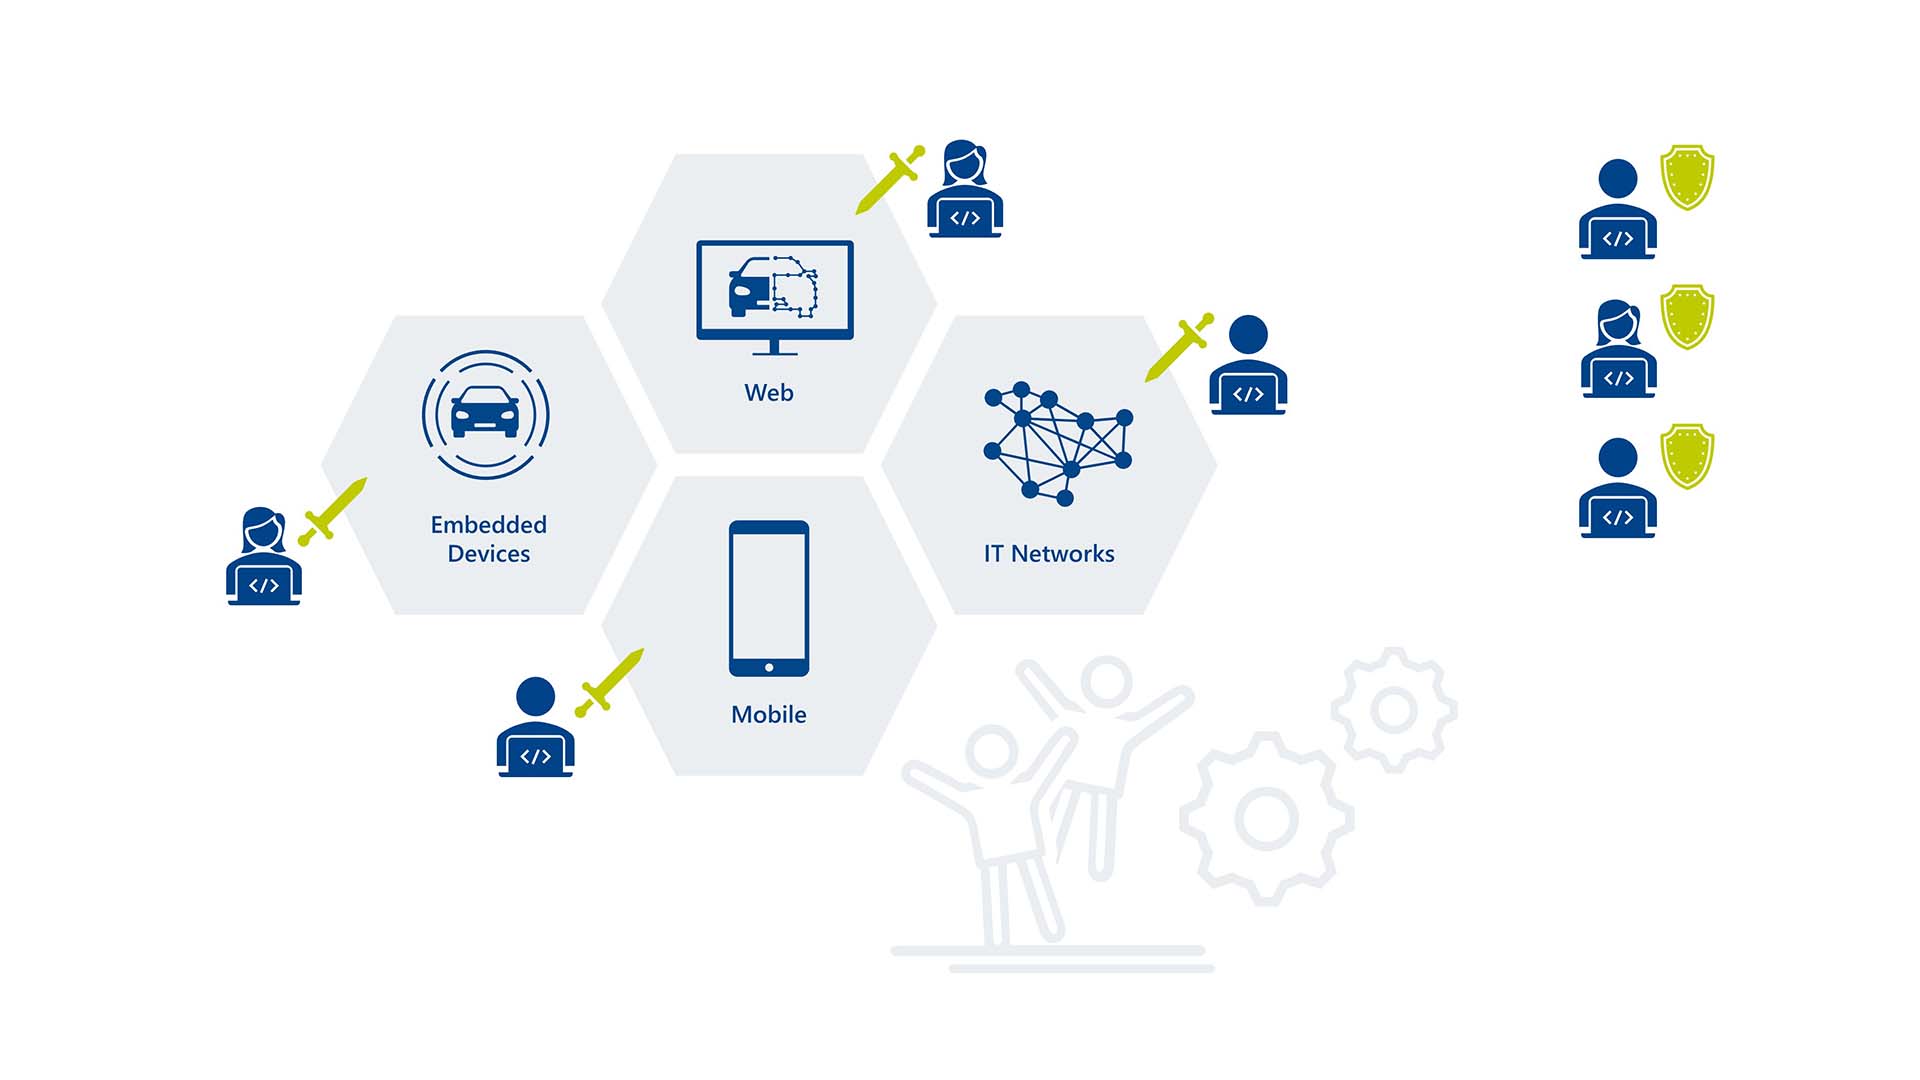
And that is why we conduct penetration tests – to ensure your systems are indeed secure.
A partner to count on for pen-testing connected systems
Testing systems holistically, in context rather than in isolation, is no easy task. This takes a diverse skill-set encompassing everything from embedded systems and cloud computing to mobile user applications and enterprise networks. ITK Engineering can help you with IT penetration testing. We also excel at testing embedded systems. Our expertise with embedded systems is a matter of record. We do indeed have a deep well of cross-industry experience in the automotive, healthcare, industrial, and other sectors to draw on. And we know all about IT systems, web and cloud services, IT networks, and smartphone applications.
ITK Engineering, a team player
We play the hacker to allow our customers to see their IT from the perspective of an intruder. This is where our role as an adversary ends. Everything else we do, particularly in projects, we do in the spirit of partnership. Simply reporting our findings is not enough – we always strive to find solutions to each customer’s unique problems. If customers wish, we can even bring them on board with the testing process. This cooperative mindset is rooted in what we do. ITK Engineering develops systems, so we are aware of all the pitfalls. Our experts have the requisite domain knowledge and know what difficulties can arise when countermeasures are taken at a late stage. And we would be delighted to share our coping strategies with you.
Your benefits at a glance:
- Technical and cross-domain skills: We have the skills to develop embedded security mechanisms, and we are an experienced partner who understands the fundamentals of your products and processes. After all, this is our day-to-day business.
- Security engineering expertise: We know how difficult it is change systems. This is why recommend strategies to minimize disruption by changing only what really needs to be changed.
- An outsider’s perspective: We are not directly involved in your product development effort, so we can give you the benefit of an unbiased perspective.
- Service in the spirit of partnership: We continue to support you after submitting our report, helping to interpret and put the results into practice.
- Involvement in penetration testing: If you wish, we will be happy to bring you on board to help steer the direction of pen-testing to wherever you want it to go.
- In-depth probing: We dig deeper, going beyond semi-automated vulnerability scanning to identify more vulnerabilities.
Our penetration testing certifications
Our pen-testing team has the following credentials: Offensive Security Certified Professional (OSCP), Offensive Security Experienced Penetration Tester (OSEP), Foundation in ISMS according to ISO/IEC 27001. Rest assured, your data and prototypes are safe with us. We have the following in-house certifications, including documentation and audit experience: TISAX Certification Level 3, ISO 27001 Certification.
Our reference projects
Embedded gateway ECU penetration test
Hybrid system penetration test (web service, mobile app, embedded ECU)
IT network penetration test
Our penetration testing portfolio
- Penetration testing for several web applications, including automotive: OWASP, OAuth, Keycloak, Kubernetes, Docker, Angular, Spring Boot, React, NodeJS, SQL – and NoSQL database, etc.
- Penetration testing for multiple enterprise networks (IT): Internal and Internet-facing service port scanning and detailed vulnerability analysis, Active Directory, AD forests, network shares, ADFS, AzureAD, ADCS, databases, custom enumeration and analysis, email phishing campaigns, AV evasion, etc.
- Embedded penetration testing (for example, for airbag systems, gateway ECUs, specialized ECUs, medical robots): Unified diagnosticservices (UDS), controlarea network (CAN / CAN-FD), LIN, automotive Ethernet, SOME/IP, DDS, DoIP, NFC, Wifi, Bluetooth & BLE, JTAG / XCP / DAP, secureboot, secure update, etc.


Contact
Dr. Jens Köhler
Cyber Security
Unsolved challenges?
Get in touch with us. Your personal contact is:
Dr. Jens Köhler
Cyber Security
* Mandatory fields